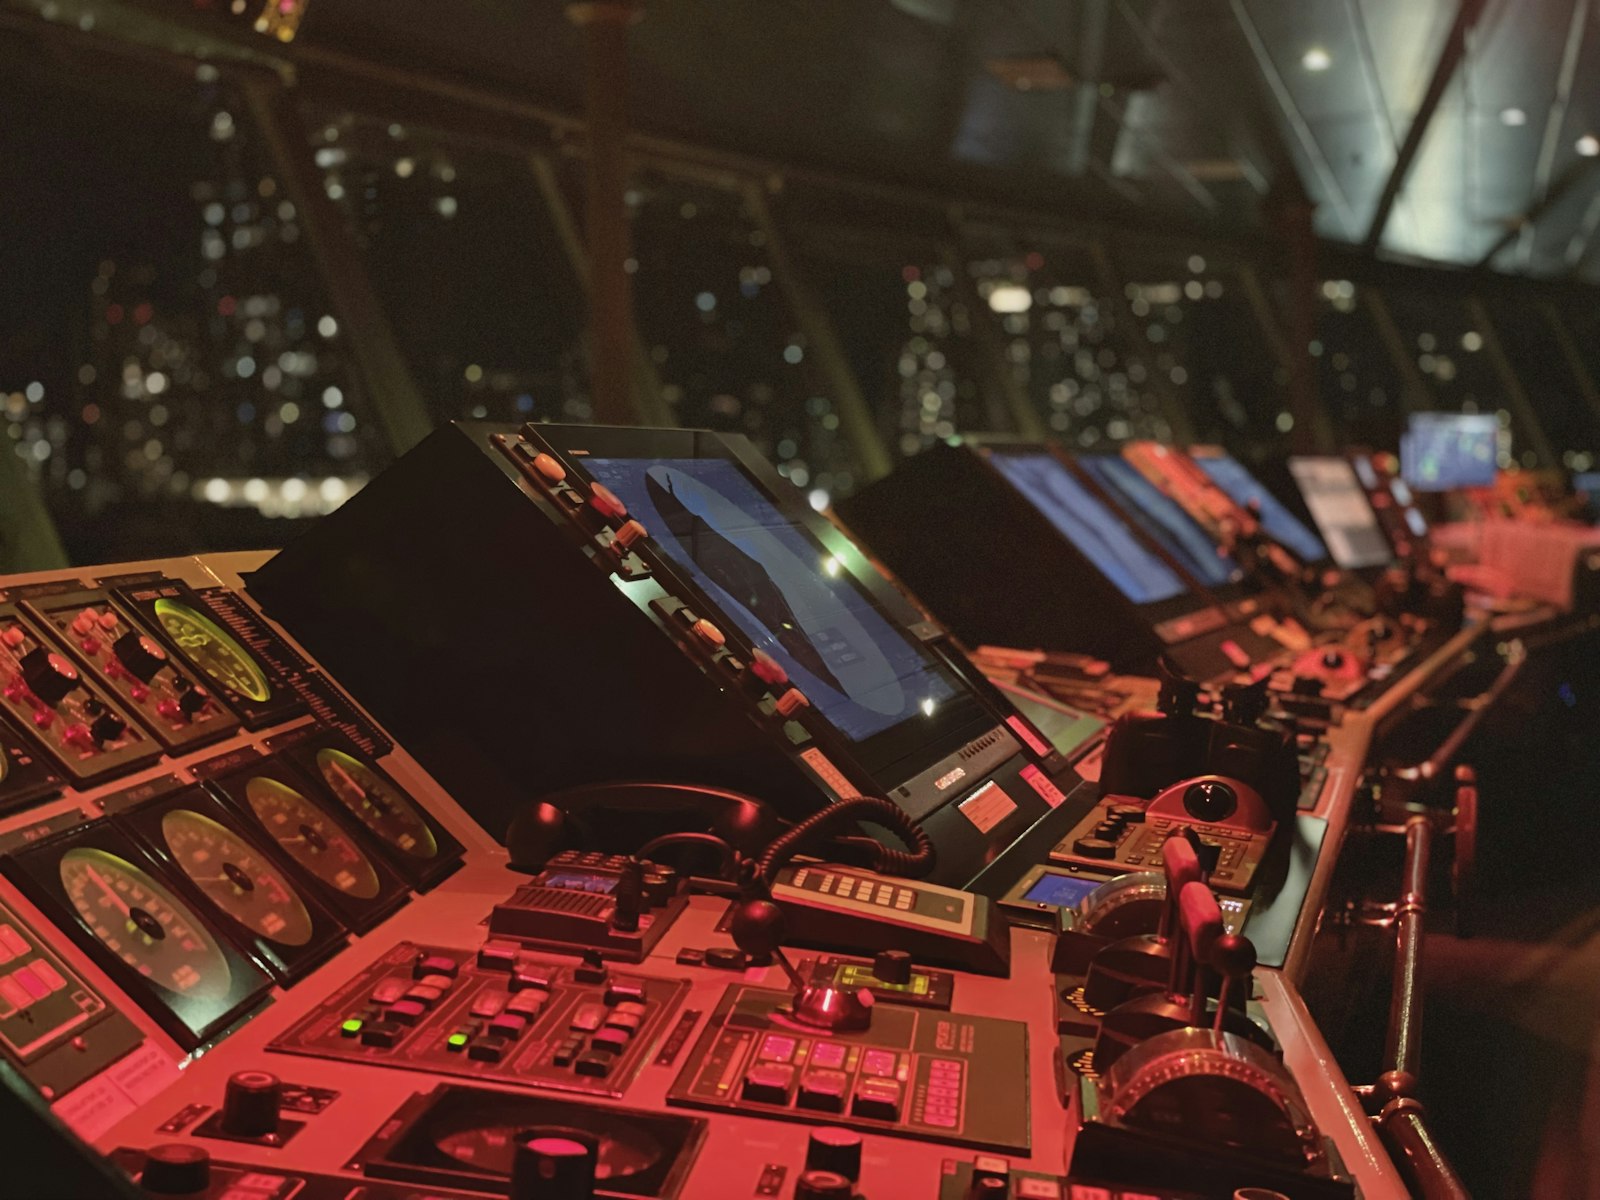
PwC UK's August 2026 insight paper, "Rewiring Enterprise Risk Management", argues that enterprise risk management has drifted into something process-led and backward-looking (PwC, 2026). Risks, on its account, are classified, reviewed on a cycle and reported through governance after the decisions that created them have already been taken. Its proposed correction rests on three shifts. The first anchors risk work in decisions themselves, where registers only record them afterwards. The second prepares for how disruption moves, since no institution can forecast every event that might hit it. The third puts artificial intelligence to work sharpening human judgement, as a tool that supports the person deciding. Set beside eighteen years at sea, each shift describes a practice already tested under the heading of operational judgement.
The pattern recurs in export control compliance and in AI governance. The frameworks now being formalised there describe practices operational institutions have exercised for decades under different vocabulary, largely because the consequences of lacking them were immediate. The Three Lines Model offers one shared vocabulary for the comparison, separating the management of risk in day-to-day operations from independent assurance over it (Institute of Internal Auditors, 2020).
Risk at the point of decision
Risk is created in decisions, formal and informal, and too often reviewed afterwards, on a reporting cycle, once momentum has become difficult to reverse (PwC, 2026). The first shift places risk expertise in the moments where choices are made, before a decision has set anything in motion. Operational institutions settled that timing question, before commitment or after it, some time ago.
At sea, command decisions do not wait for a quarterly committee, so risk judgement is exercised at the point of decision or not at all. The operational planning process forces assumptions into the open before commitment. The brief-back, in which a subordinate states the plan and its risks back to the commander, builds challenge into the decision itself. In first-line assurance practice the same logic holds. A findings register that feeds decisions within the operating cycle, while the consequences remain cheap to change, is doing risk work in a way that a register compiled for a report may not.
Defence assurance also contains the pattern PwC warn against, in the periodic inspection that examines compliance after the fact and the annual audit cycle that reports on decisions long since locked in. The critique therefore cuts both ways, and Defence has plenty left to learn. The decision-focused model already exists in the operational half of these institutions. The work is to extend it into the assurance half, without importing it from outside.
Float, move, fight
The second shift introduces what PwC term the Minimum Viable Company: the smallest set of services, processes and dependencies that needs to keep working for an organisation to remain viable under severe stress (PwC, 2026). Leaders are asked to define what should be protected, preserved and restored when several things fail at once, a change from trying to predict every disruption. The shift moves a risk function away from forecasting and towards prioritisation, and in doing so it changes what the function is for.
When a ship takes damage, the priorities are to float, to move and to fight, in that order, and every damage-control drill rehearses the dependencies beneath those three outcomes. Readiness states, mission-essential equipment schedules and minimum manning requirements can each be read as an answer to the question PwC now ask boards to consider. I led the regeneration of a supply chain department to readiness for sea, and it followed the same sequence. It rebuilt to a defined minimum viability and then beyond it, dependency by dependency, each tested under stress before it was trusted.
The same lens can be turned on compliance itself, by asking which checks protect safety and operational effectiveness and which persist because a process once demanded them. The two applications presuppose one another. An organisation can reduce its checking safely only if it already knows which dependencies bear upon its viability. Once the minimum viable organisation has been defined, reducing the assurance burden around everything outside it becomes a natural next step. One is the concept and the other its consequence in practice.
The officer still decides
The third shift holds that AI should extend the reach and imagination of risk functions. It would detect weak signals, test assumptions and generate scenarios at pace, while the consequential judgements remain human, since those involve ambiguity, incomplete information and behaviour under pressure (PwC, 2026). The maritime domain reached this settlement long ago. The sensor picture has grown enormously, and the officer of the watch still decides. On that reading, the value of AI in risk work is a wider field of view, and the assurance question that follows is how an organisation evidences that the tools amplifying its judgement are themselves trustworthy.
Around a quarter of technology executives had enterprise-wide AI governance and ethical oversight in place for agentic AI, and roughly a third had ensured high-quality, accessible and governed data (EY, 2026). More than three quarters expected AI investment to rise by at least twenty per cent over the following year. Investment is therefore expected to grow faster than the governance around it. That is the space in which ISO/IEC 42001 and, in Defence, JSP 936 earn their place, since both exist to make trustworthiness demonstrable.
What a junior rate can stop
PwC close by asking risk functions to replace vague talk of risk culture with specific observable behaviours (PwC, 2026). These include whether leaders invite challenge early enough, whether weak signals are escalated and whether assumptions are tested while there is still time to change course. A year spent making this argument within the supply chain profession suggests one further distinction, between compliance as behaviour and compliance as understanding. A checklist can be completed without being understood, and a unit can pass an inspection while holding no clear view of the risk the inspection exists to detect. A behaviour, by contrast, can be observed, coached and improved. Near-miss reporting, brief-backs and the willingness to let a junior rate stop a process they believe to be wrong are all behavioural interventions, and they long predate the language now used to describe them.
Psychological safety has been linked to learning behaviour in work teams (Edmondson, 1999), which points to a condition no framework supplies. Assurance runs on data, and data is entered by people. Where an individual believes that reporting a problem honestly will cost them, the system may receive a compliance performance in place of the truth. Every downstream analytic, AI-derived insight and credential resting on that record would inherit the error. In my view, psychological safety is a precondition of assurance, because every record depends on someone being willing to report honestly.
Before the next scheduled review
Naval and corporate risk management differ most in timing. At sea, risk expertise tends to enter before a decision is committed, because the consequence can arrive within the watch. The pattern PwC describe brings it in afterwards, on a reporting cycle (PwC, 2026). My own view, from eighteen years in Defence logistics, is that the point at which risk enters a decision is the most telling single measure of whether an organisation is managing risk or reporting on it.
Two-way traffic
The three shifts describe practices naval operations already run, and naval assurance still shares some of the habits PwC criticise. Corporate risk management is rewiring itself towards practices that institutions operating under immediate consequence developed from necessity, so the learning should flow in both directions. Defence could adopt the discipline of naming, measuring and maturing what it currently does by instinct, since a practice that is never named is seldom taught, assured or improved deliberately. Industry could study institutions in which risk management was never optional and the feedback loop was rarely longer than a watch. Practitioners who cannot name what they are doing may struggle to defend it, transfer it or recognise it when a consultancy sells it back to them under a different label. Naming the practice comes first.
The views expressed here are my own and are based on general observations about enterprise risk, logistics assurance and governance. They draw only on published sources and do not represent the position of the Royal Navy, the Ministry of Defence or any organisation with which I work. Nothing published here reproduces any organisation's internal policy, procedure or assurance output.
References
- PwC UK, Rewiring Enterprise Risk Management, insight paper, August 2026.
- EY, Five shifts reshaping the agentic AI economy in 2026, drawing on the EY global technology executive survey, 2026.
- ISO/IEC 42001:2023, Artificial intelligence management systems.
- JSP 936, Dependable Artificial Intelligence in Defence (GOV.UK).
- The Institute of Internal Auditors, The IIA's Three Lines Model, 2020.
- Edmondson, A. (1999), "Psychological Safety and Learning Behavior in Work Teams," Administrative Science Quarterly.